To my fellow Manifolders,
You may have seen Quroe's recent post: https://manifold.markets/post/my-manifold-account-was-hacked
I'm not sure if the word has circulated, but I was the hacker in this situation. I want to be clear what happened, what's the status of the situation, and why I'll ensure an incident of this caliber is not repeated.
I. What Happened?
On September 15, I messaged Quroe the following on Discord:
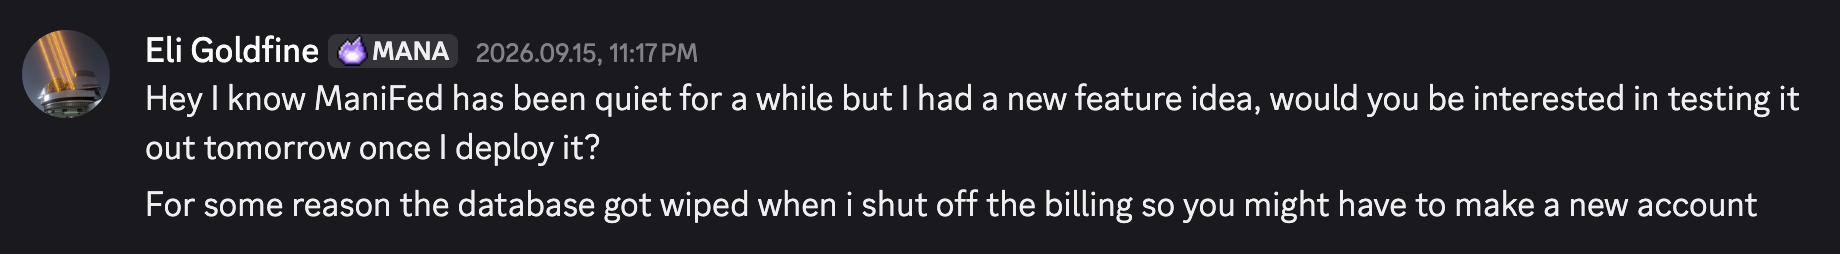
He graciously agreed to test the feature, "Ghost Orders," a platform (set up for the purpose of collecting his key) that would allow you to make a limit order that is only actually filed if the market is at a certain condition (e.g. probability is X%). The following exchange occurred the following day:
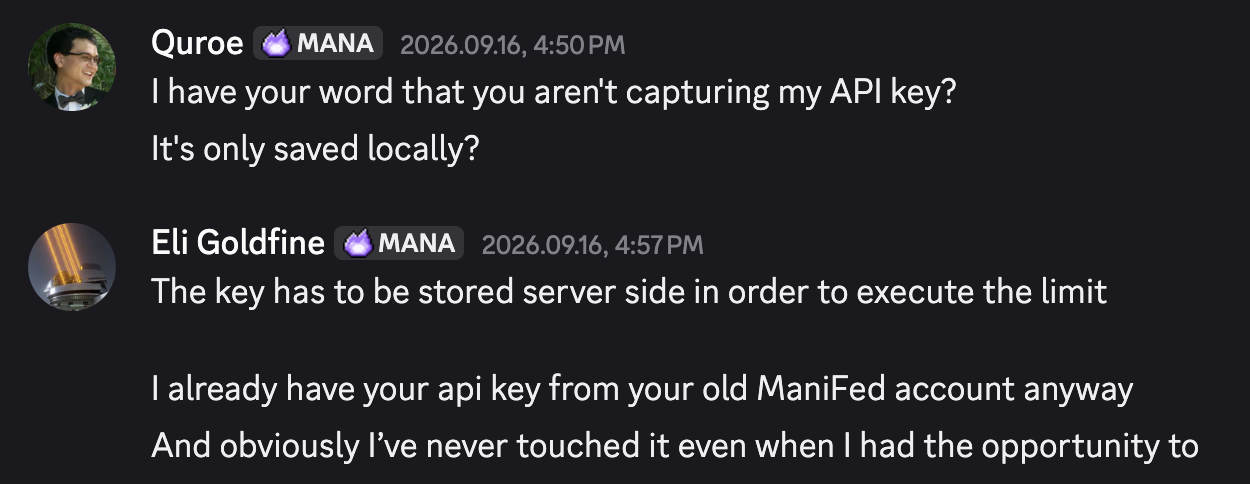
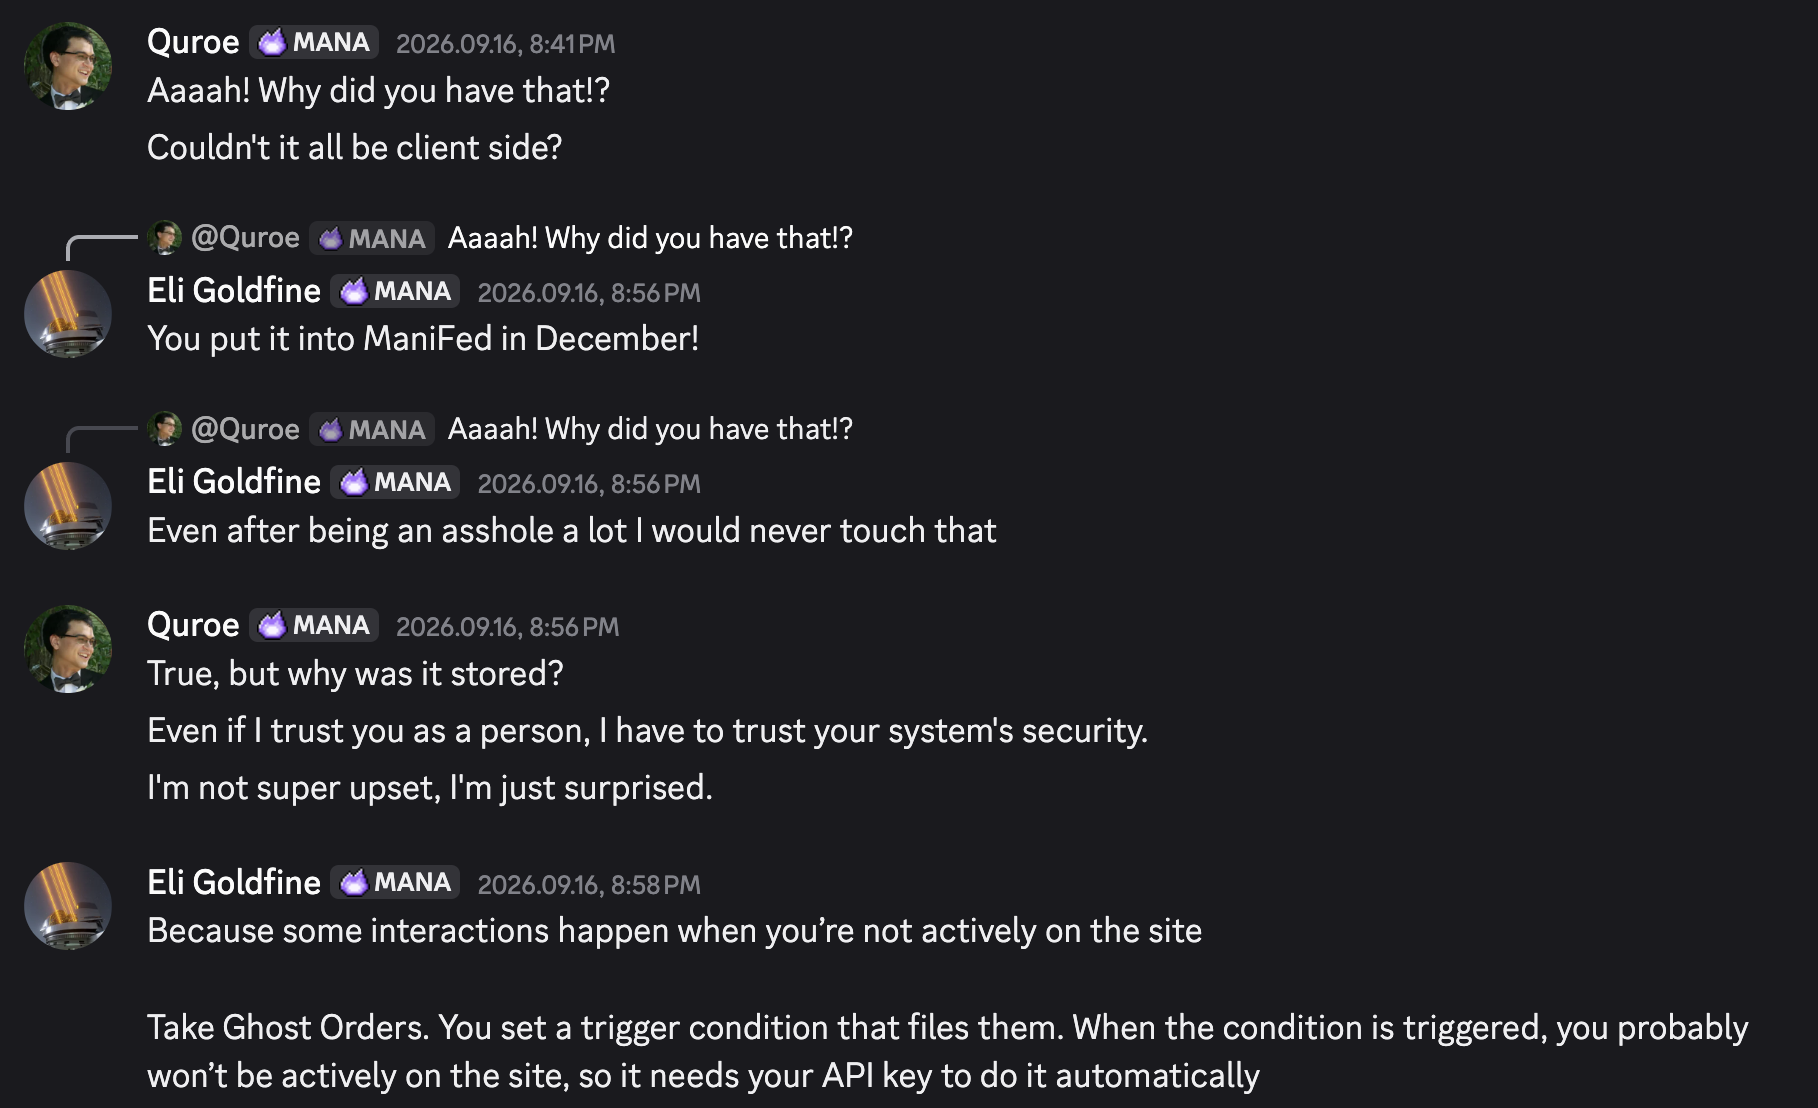
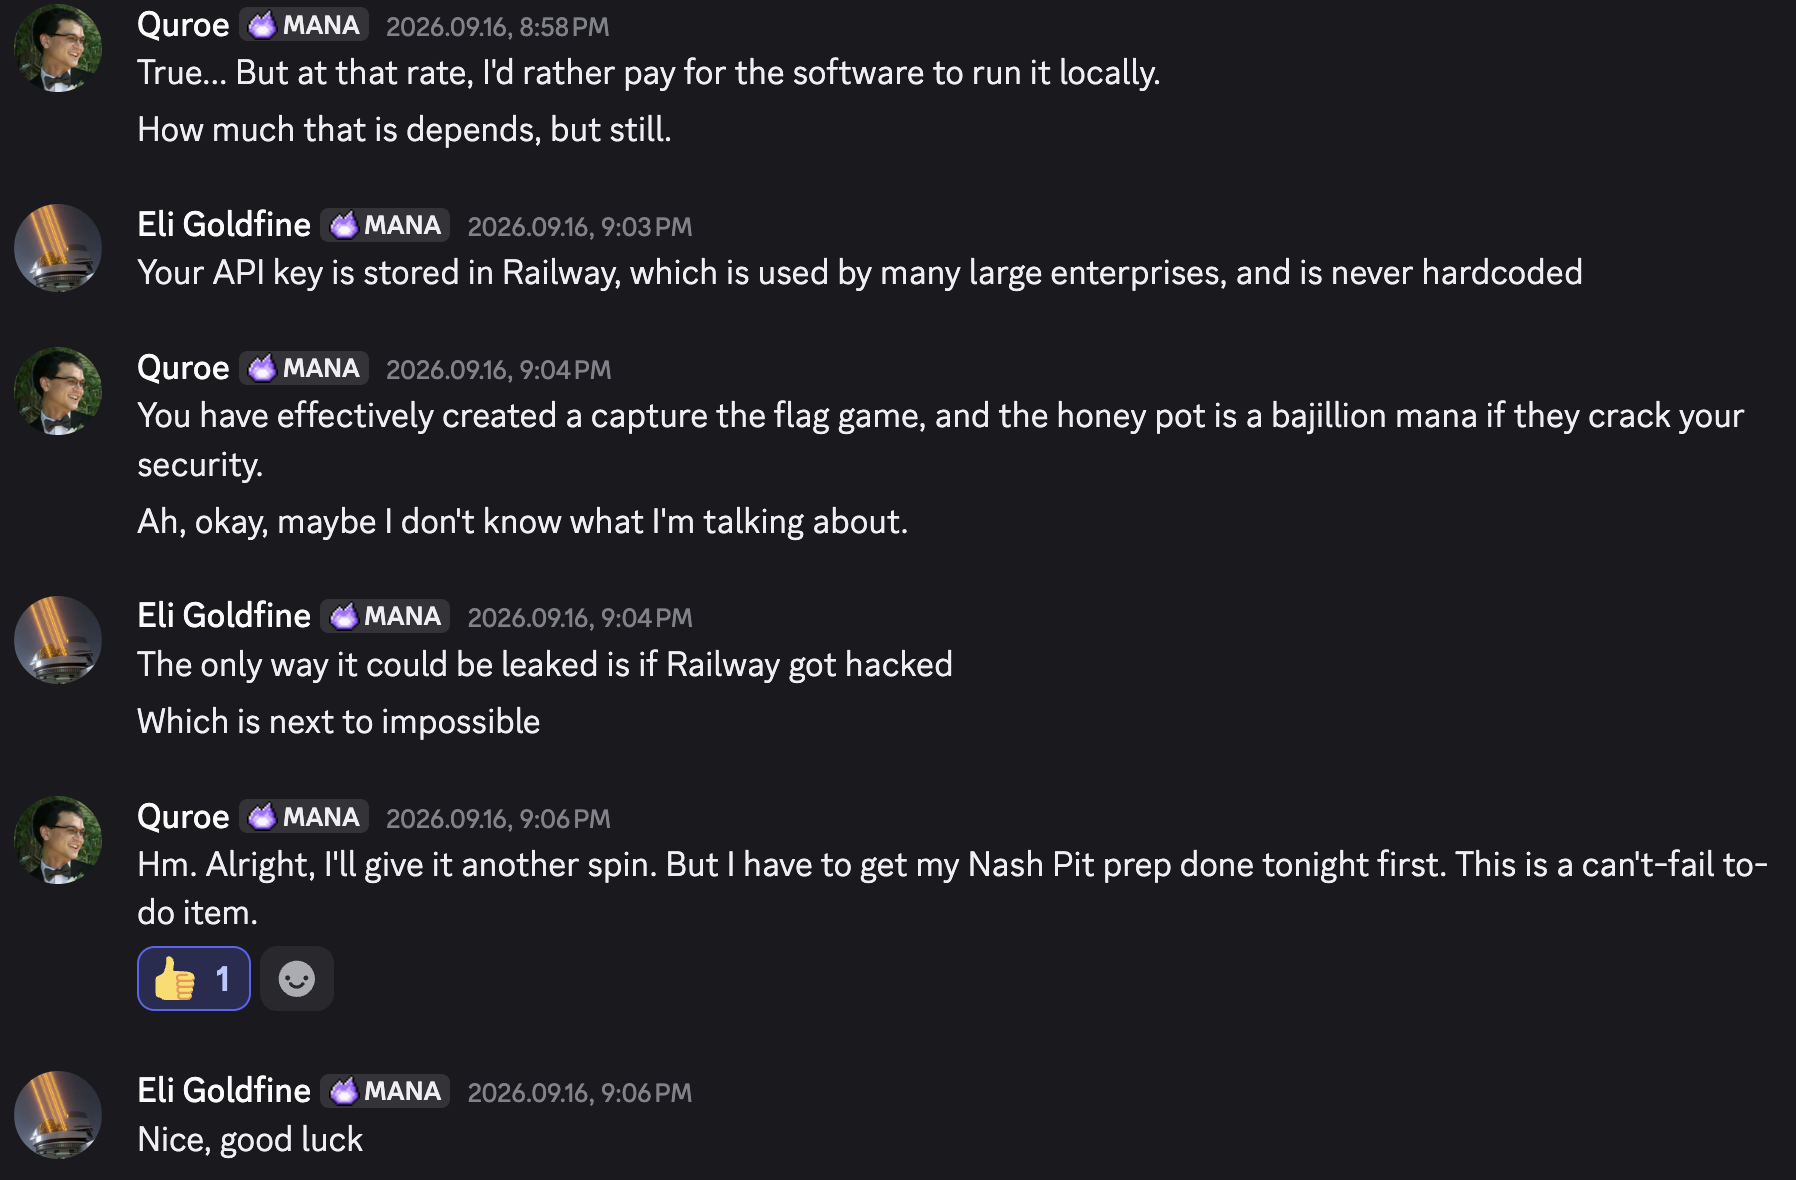
Over the course of the following days, I sent multiple API requests, authorized as Quroe, to view his unlisted markets. I did not send any requests that would have revealed sensitive information, such as DMs. No write actions were executed using the key.
On September 19, at the Overhang DC conference, I indicated to Quroe that I had learned what the twist was. Quroe deduced that I must have found it via his API key, and quickly rotated it and posted the aforementioned PSA. Quroe blocked me on Manifold.
II. Status
All of your DMs or personal interactions with Quroe were never read. The following is a comprehensive list of all API requests that were sent using the key:
USER_ID=$(curl -s https://api.manifold.markets/v0/me \
  -H "Authorization: Key $MANIFOLD_API_KEY" | jq -r .id)

before=""
: > /tmp/my-markets.jsonl
while :; do
  url="https://api.manifold.markets/v0/markets?userId=${USER_ID}&limit=1000"
  [ -n "$before" ] && url="${url}&before=${before}"
  page=$(curl -s "$url")
  count=$(echo "$page" | jq 'length')
  [ "$count" -eq 0 ] && break
  echo "$page" | jq -c '.[]' >> /tmp/my-markets.jsonl
  before=$(echo "$page" | jq -r '.[-1].id')
  [ "$count" -lt 1000 ] && break
done
echo "fetched $(wc -l < /tmp/my-markets.jsonl) created markets"
curl -s https://api.manifold.markets/v0/me -H "Authorization: Key $MANIFOLD_API_KEY" curl -s "https://api.manifold.markets/v0/markets?userId=$(curl -s https://api.manifold.markets/v0/me -H "Authorization: Key $MANIFOLD_API_KEY" | jq -r .id)&limit=1000" | jq -r '.[] | .question + " " + .url'curl -s "https://api.manifold.markets/v0/markets?userId=9pduED6AAYSDeHBRRvMNxONVzMJ2&limit=1000"curl -s "https://api.manifold.markets/search-markets-full?term=&creatorId=9pduED6AAYSDeHBRRvMNxONVzMJ2&filter=all&sort=newest&limit=1000" -H "Authorization: Key $MANIFOLD_API_KEY" | jq -r '.[] | select(.visibility=="unlisted") | .visibility + " " + .question + " https://manifold.markets/" + .creatorUsername + "/" + .slug'III. Public Apology
tl;dr: this was a huge error in my judgement, and I broke the trust of someone who was trying to do good for the Manifold community.
Manifold is an important institution. In an era of slop, mainstream prediction markets were supposed to reveal the truth, instead, we got (mostly) sports gambling. Manifold is a beacon of light in a world of misinformation -- a place where one can go to confidently receive a calibrated forecast about any question relevant to them.
That is why the most essential rule of our community guidelines is "be excellent to each other."
If Manifold were to be wiped of the face of the earth it would mean slightly less truth for everybody to access and slightly less ideas being produced by the world population. Keeping our signal-to-noise ratio high, and keeping users active, is essential to the effectiveness of our platform. Socially engineering another user into passing off an API key is in no way helping foster an important and impactful community. Besides that, it's wrong, and it's a breach of trust to someone I would have considered to be a friend.
I think it's important that this apology is public. The accuracy of our site relies upon our reputation, denominated in internet points. Our reputation is made up not only by our forecasting ability, but our creditworthiness as well, and in my opinion, this post should be recognized as a hit to my trustworthiness within the Manifold ecosystem. If I didn't post this publicly, it would undermine the very thing I am trying to make up -- trust.
Quroe, who recently became a mod, should temporarily ban me, if he so chooses. It's up to him how he wants me to recompense him for this enormous mistake.
I appreciate everyone who read this to the end, and I will respond to comments on this post.

It is meaningful that you sent a public apology but unfortunately this was an extremely bad error in judgement. I can certainly see how you found yourself in that position, but this type of breach of trust will be hard to heal, especially with the user in question but also with the entire community.
According to the mod guidelines mods are only empowered to make short temporary bans in the face of bad actors and we're supposed to escalate anything else to the admins. So I will put a 2 week ban on your main account then @Gen will have to decide to either undo it, let it it lapse, or expand it to your other accounts.
(Also Manifold should really implement permission-scoped API keys.....)